The Australian Securities and Investments Commission sued Fortnum Private Wealth in July 2025 after the AFSL reported a data breach suffered by a recently added practice, Perth-based Wealthwise. The breach prompted ASIC to begin further investigations into Fortnum’s cyber security practices and policies.
Fortnum had issued its first cyber security policy in April 2021, which applied to its authorised representatives and covered various aspects of security, including that sensitive client information was to be stored in the Xplan platform.
It also included optional steps based on the Australian Cyber Security Centre’s Essential Eight framework. These were self-assessments and attestations, which were supposed to be completed by advice practices by September 2021, but which were not enforced. Due to, among other factors, the low rate of completion, Fortnum decided to revise its policy.
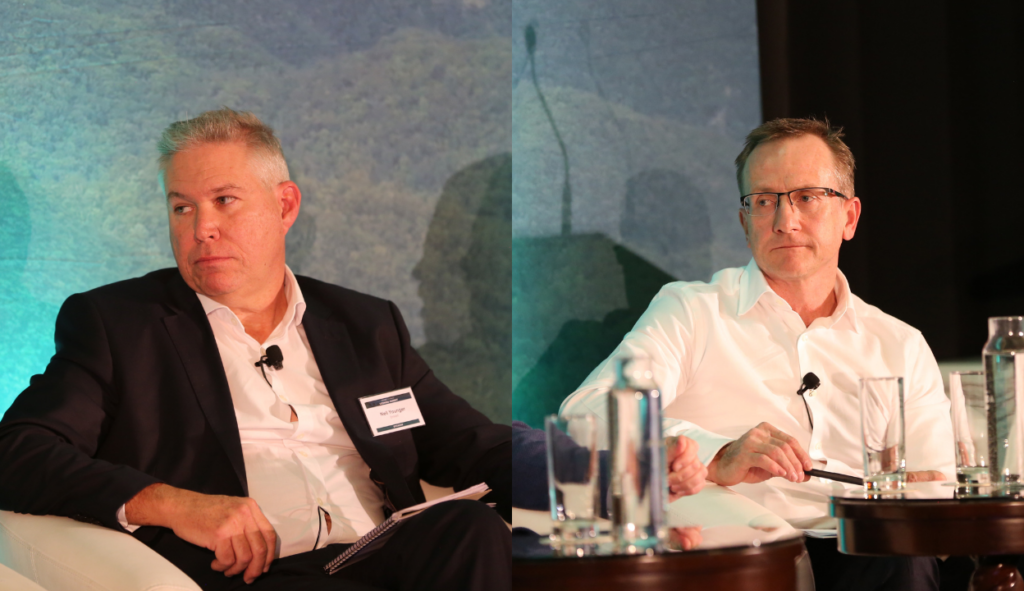
The updated cyber policy, which would go into effect in May 2023, mandated not only that its ARs must have adequate insurance but also that managed services providers (MSPs) engaged by the practices also had adequate insurance “to be able to respond to instances that we knew would continue to occur, because no matter what controls you put in place, you’ll have a cyber issue,” Entireti group chief executive officer Neil Younger tells Professional Planner.
“We mandated the types of education programs the advisers had to attend and extended those to include support staff in their offices.”
In a statement previously provided to Professional Planner, Fortnum chief executive officer Matt Brown said significant enhancements had been made since the period of ASIC’s review.
“We have strengthened our cyber governance framework through substantially revised cyber policies, stronger mandatory cyber controls, annual cyber reviews by specialist providers, enhanced audit and monitoring arrangements’ regular cyber training for advisers and employees, additional cyber resources and support and the appointment of a dedicated head of cyber security across the group,” Brown said.
He tells Professional Planner that the head of cyber security is “a cyber expert who sits in our technology team, but whose lens is cyber governance, security, and support”.
Younger says the expert “looks after all of our group-level cyber obligations”.
“So, we’re holding data, and he looks after that [which is] corporate and looks after all of the policy settings as they apply to advisers.”
Fortnum also mandated how client data is moved, and “all personal information sent between parties must be encrypted or through a portal”, Younger says.
The new policy also mandates that each practice has a cyber response plan – a step-by-step document that states who is responsible for what if a cyber breach occurs and the steps to be followed when responding to an incident.
Fortnum assists practices with that by structuring a framework aligned to its policy’s requirements.
“Having a cyber response plan that’s documented, that is clear, that all the people in the office are trained on it, that we provide the infrastructure within, they can build such plans that are executable and readily done and available. So we teach them how to do that,” Brown tells Professional Planner.
Fortnum also has a panel of MSPs that practices can choose from if they don’t want to search for one on their own. The licensee negotiates commercial rates and lists only MSPs that understand Fortum’s policies and work well with the systems required.
The latest piece of the puzzle is a diagnostic tool that will monitor practices 24/7, which will be in place by February 2027.
Ultimately, what was provided to practices as guidance has now been mandated, with Fortnum making it clear to its ARs there will be no tolerance for those not following the rules.
For Younger, the biggest lesson for licensees from Fortnum’s experience is to have the required expertise, document all the steps taken, and have the capability to enforce a standard when it’s put in place.
“You need to be able to supervise it adequately, and they’re the critical pieces,” he says.
The cost to practices of using a better MSP, buying insurance and being on top of all the requirements adds up quickly but Younger says that’s where “we’ve seen a maturity in the sector that is pleasing, which is the practices are now thinking like businesspeople, and these things are not just imposed upon them, they’re necessary to run a business”.
“But some in the sector still feel that cost is imposed upon them, and they’ll do things to avoid it. And that is bad, not just for that practice and for the clients attached to that practice, but it’s bad for the ecosystem.”
Younger and Brown say that the onboarding of new practices across the network now also assesses the risk of those businesses from a cyber perspective, which includes compliance with Fortnum standards on transition, and conducting due diligence on third-party providers, to avoid similar issues arising again.
Why these changes are important
Independently of which party gets breached, ultimately it is the AFSL that is responsible. Fortnum’s first cyber security policy was developed by its then-head of technology. But, according to court documents, during the period of the contraventions (20 April 2021 and 11 May 2023), Fortnum did not employ anyone with specialised qualifications, experience or expertise in cybersecurity.
That included the head of technology who “had a formal educational background in business and financial planning and had gained relevant experience in technology roles across various financial services organisations but did not have any formal cybersecurity training”.
Fortnum failed to engage with specialised third parties although it did use external IT consultants.
The policy received input and feedback from Fortnum leadership team and approved by its risk and compliance committee whose head at the time was Younger, along with Fortnum’s head of advice and head of operations.
“The board of Fortnum was aware that there had been low completion rates for both the self-assessment and the attestation by at least 5 September 2022,” according to court documents.
Based on the documents, it was after receiving a letter from a Fortnum AR regarding an earlier cyber case involving the Insignia Financial-owned licensee RI Advice, which was finalised in May 2022, that Fortnum started a deeper review of its first cyber-security policy.
Future risks
Brown says that the experience has sharpened the executive team’s and directors’ focus on cyber security issues.
“I’m a director on the Fortnum licence, and Neil’s a director. We’ve got other directors on the group licences, but it’s sharpened our view in how we deal with, not the next wave of cyber insecurity, but the next wave of technology innovation around AI, and having an AI policy. How do you use that game-changing, wonderful opportunity in a safe and reliable, consistent environment?”
He says this has informed the group’s strategic thinking and helped them build an advice platform that in part solves the security of using generative and deterministic AI.
“The point is that it that it does sharpen our thinking,” Brown says. “And to be honest, deepens our understanding. We’ve been forced to roll the sleeves up and understand technology in areas that [we didn’t].”
Younger says there is a lot of noise in the market around productivity tools that can be used by advisers, who must be cautious about which they use, and how they use them.
“Advisers, so thirsting for productivity, don’t necessarily know where the data goes, and invariably it’s dealing with personal information, and they don’t necessarily have the ability or the skills to validate the output of those tools,” he says.
“So you get caught in this catch-all world of you’re regulated and you provide advice and you’ve got a best interest provision. All the provisions that apply to cyber are actually provisions that were built for [delivering] advice. The same rules – ‘efficiently, fairly, and honestly’ – they’re a catch-all piece that applies to operating risk, because we need the data to deliver the advice.
“Now you take that AI lens into the conversation. You’re going to suddenly [have] an adviser picks one of these tools off the street, and I’ve got to know that they’re doing it. So we do have policy settings around what it can be used for. We do have approval processes for tech that sit structure, and we are investing considerably in an ecosystem that can check the output of our tools real-time.”
What led to ASIC’s lawsuit against Fortnum
The Supreme Court of NSW ruled on 12 October that Fortnum was to pay $1.35 million to ASIC plus $250,000 in costs for failure to do all that was necessary to ensure the financial services covered by the AFSL had adequate cyber security policies to manage and mitigate risks to its authorised representatives.
The court found that Fortnum’s risk management system did not adequately identify and evaluate cybersecurity risks for itself and its ARs and did not establish, implement and maintain controls to manage those risks.
Furthermore, there were several events that Fortnum was or should have been aware of including:
- In February 2020, a principal practice operated by one of Fortnum’s directors experienced a cybersecurity incident arising from a phishing link.
- On or around 26 January 2021, the email address of an authorised adviser of one of Fortnum’s then-principal practices was compromised by malware, resulting in a spam email being sent to the authorised adviser’s email contacts.
- Between March and April 2021, the email address of an employee of one of Fortnum’s then-principal practices was accessed without authorisation by an overseas IP address. An email forwarding rule was created and subsequently removed 26 hours later during which time 16 emails were sent but returned as unsuccessful.
- On or around 1 July 2021, the email address of an AR of one of Fortnum’s then-principal practices was accessed and an impersonation email was sent to certain Fortnum staff, attempting to gain unauthorised access to Fortnum systems.
- On or around 26 July 2022, two employees of one of Fortnum’s principal practices clicked on malicious phishing links which resulted in an unknown threat actor gaining access to at least one employee’s email account and sending 1266 emails containing phishing links from that employee’s account. Fortnum was aware of the incident by no later than 30 August 2022.
- Before Fortnum revised its policy in May 2023, several of its ARs experienced cyber incidents. One of these was Wealthwise who suffered a major data breach in September 2022, which resulted in the exfiltration and publication of over 200 gigabytes of data relating to up to 9,828 clients. The breach involved primarily clients who had been serviced before Wealthwise became a principal practice of Fortnum. Fortnum monitored the breach at first being advised there had been no loss of client data but finding out months later the data had been released on the dark web. Fortnum reported the incident to ASIC and to the Office of the Australian Information Commissioner.
Risks to licensees
At the time of the contraventions Fortnum had around 22 employees but up to 94 financial advice practices, more than 200 authorised advisers, and around 55,000 retail clients. To perform their jobs and be compliant under industry’s regulations, these practices collected and kept highly sensitive personal information, including identification documents, tax file numbers and financial account details.
Justice Black said Fortnum exposed its ARs and its ARs’ retail clients to the risk of cyber-related attacks and cybercrime, the consequences of which could include serious harm and loss.
“And did not meet the reasonable standard of performance that the public is entitled to expect from the holder of an AFSL.”
ASIC chair Sarah Court said in a statement Fortnum was aware of the cybersecurity risks facing its business and authorised representatives but failed to implement an adequate cybersecurity policy and have adequate oversight and monitoring arrangements.
“This outcome reinforces ASIC’s continued focus on licensees getting the fundamentals right. Strong cyber resilience is critical to maintaining trust and confidence in our financial system. We will continue to work with industry to lift standards and take action where businesses fall short,” Court said.


Leave a Comment
You must be logged in to post a comment.